
TL;DR
Maersk confirmed unauthorized access to and data extraction from a local legacy system inherited from a previous acquisition. BleepingComputer reports that the WhiteArmor ransomware group claims it has about 100 GB of data and is demanding $5 million; Maersk has not confirmed those claims.
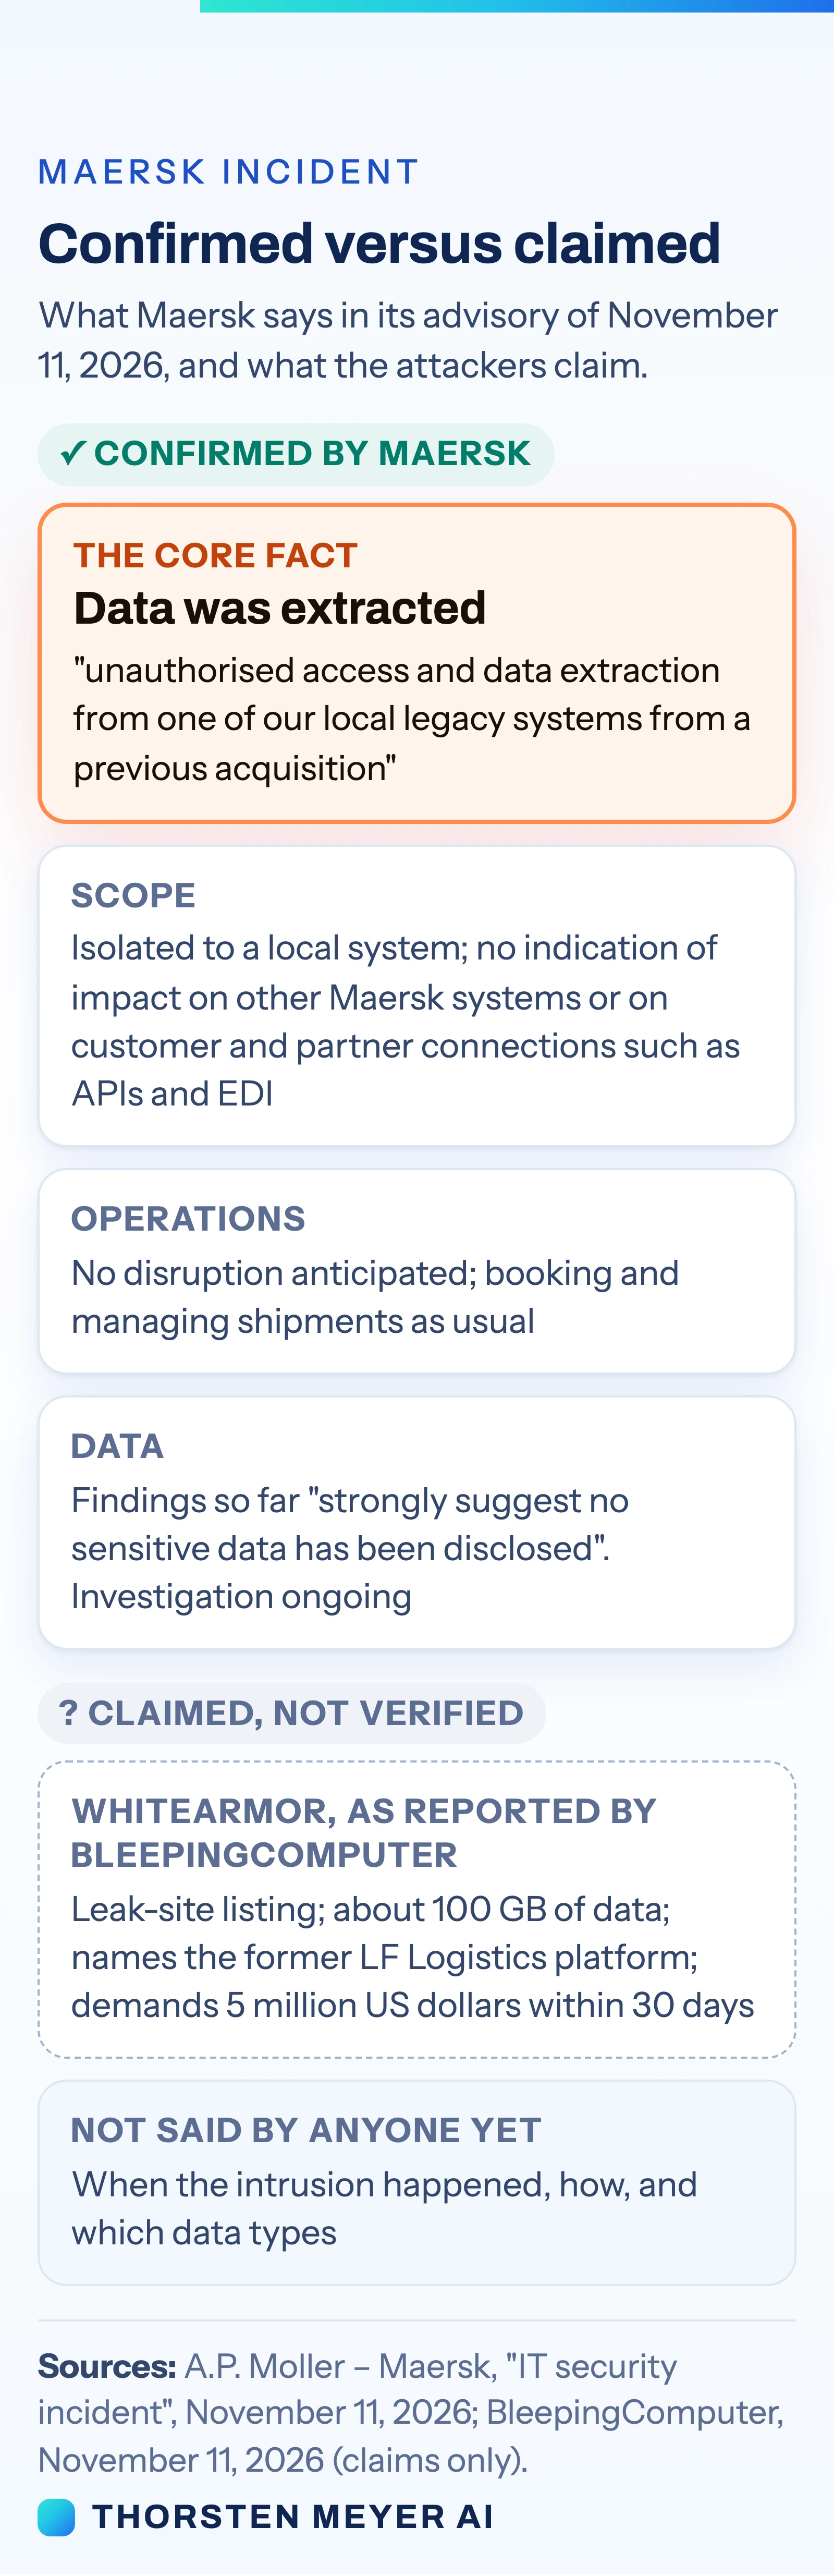
A.P. Moller–Maersk confirmed on November 11 that someone gained unauthorized access to and extracted data from a local legacy system associated with a previous acquisition. BleepingComputer reported that the ransomware group WhiteArmor claims it holds about 100 GB of data and is seeking $5 million, but Maersk has not confirmed the group’s identity, ransom demand or account of what was taken.

Get business pricing on tech for your team
- Business-only prices and quantity discounts
- Tax-exempt purchasing
- Multiple users, one account, clear invoices
Maersk said its cybersecurity team discovered the issue, launched an investigation and took steps to secure the affected system. The company’s findings so far “strongly suggest no sensitive data has been disclosed.” It said it had found no indication that the incident affected other Maersk systems or customer and partner systems connected through integrations such as APIs and electronic data interchange (EDI).
The company said it does not anticipate disruption to customer operations and that customers can continue using Maersk platforms to book and manage shipments. It said it would provide updates as relevant information becomes available and notify impacted parties if needed. Its advisory did not name the system, the previous acquisition or the date of the intrusion.
The ransom and stolen-data figures come from BleepingComputer’s November 11 report, which attributed them to WhiteArmor’s leak-site listing. The group reportedly claims to have approximately 100 GB of data and has demanded $5 million. Those claims have not been independently confirmed in the supplied source material, and Maersk’s advisory does not mention WhiteArmor or a ransom.
What Maersk Customers Should Know
For businesses shipping with Maersk, the company’s current guidance is that bookings and shipment management can continue as usual. Maersk says it has found no indication of effects on its wider systems or on customer and partner connections, which include APIs and EDI. That is a statement about the findings so far, while the investigation remains open.
The confirmed extraction of data still creates unanswered questions for any parties whose information may have been stored on the affected system. Maersk has not identified the data involved or said whether specific customers or partners were affected. It advises customers to treat unexpected communications about the incident with caution and verify them through their usual Maersk contact.
Products Worth Considering

Bose TV Speaker Compact Soundbar with Bluetooth and HDMI-ARC, Black

Logitech MX Keys S Combo Wireless Keyboard and Mouse, Graphite

Apple Watch SE 3 GPS 44mm Smartwatch
As an affiliate, we earn on qualifying purchases.
The Legacy-System Link
Maersk described the affected system only as a local legacy system from a previous acquisition. The attacker’s alleged connection to LF Logistics is a separate claim reported by BleepingComputer; Maersk has not said which acquisition was involved.
Maersk completed its purchase of LF Logistics on August 31, 2022. At the time, it described the Hong Kong-based company as having 223 warehouses, which would bring Maersk’s global facilities total to 549, and a workforce of 10,000. That history provides one possible point of reference for the attackers’ reported use of the term “OCF/LF Logistics platform,” but it does not establish that LF Logistics systems were involved in this incident.
““unauthorised access and data extraction from one of our local legacy systems from a previous acquisition.””
— A.P. Moller–Maersk
The System and Data Remain Unknown
Maersk has not disclosed which system was accessed, which acquisition it came from, when the intrusion occurred or what data was extracted. It has not explained what it means by “no sensitive data has been disclosed,” including whether that refers to publication, access by the attackers or another measure.
WhiteArmor’s reported claim that it holds about 100 GB of data and its $5 million demand remain allegations attributed to the group by BleepingComputer. The available material does not confirm that the group carried out the intrusion, that its claimed data volume is accurate, or that the information was published. BleepingComputer reported that it had asked Maersk for additional details and had not received a response by publication.
Maersk Investigation and Customer Updates
Maersk says its investigation is ongoing and that it will update customers when relevant information becomes available. The company also says it will inform impacted parties if it finds that notification is needed. Any further information from Maersk may clarify the affected system, the data involved and whether customers or partners require specific steps.
Until then, Maersk advises customers to keep using its platforms as usual, monitor its communications and verify unexpected messages through their normal Maersk contact. The claims reported from WhiteArmor’s listing should remain attributed to the group unless Maersk or other reliable evidence confirms them.
Key Questions
What did Maersk confirm?
Maersk confirmed unauthorized access to and data extraction from a local legacy system associated with a previous acquisition. Its investigation is ongoing.
Did Maersk confirm a $5 million ransom demand?
No. BleepingComputer attributed the $5 million demand to the WhiteArmor ransomware group. Maersk’s advisory does not mention a ransom or the group.
Are Maersk shipments or customer connections affected?
Maersk said it does not anticipate disruption to customer operations and has found no indication of effects on its other systems or customer and partner connections, including APIs and EDI. Its findings may change as the investigation continues.
Was LF Logistics involved?
That has not been confirmed. BleepingComputer reported that the group referred to an “OCF/LF Logistics platform,” but Maersk has not identified the acquisition or system involved.
What should Maersk customers do?
Maersk says customers can continue using its platforms to book and manage shipments. It advises them to treat unexpected incident-related communications cautiously and verify them through their usual Maersk contact.
Source: Thorsten Meyer AI